%22%3E%0D%0A%3Cpath d=%22M76.678 2.56445H31.5757C14.1489 2.56445 0 16.723 0 34.12V124.386C0 141.866 14.1489 155.941 31.5757 155.941H76.7195C97.8807 155.941 117.05 147.347 130.909 133.479C144.809 119.652 153.356 100.428 153.356 79.2528C153.315 36.9019 119 2.56445 76.678 2.56445Z%22 fill=%22%2356E16C%22/%3E%0D%0A%3Cpath d=%22M276.422 11.9103L186.549 101.844C166.592 121.815 180.74 155.986 208.955 155.986H298.828C316.338 155.986 330.528 141.786 330.528 124.265V34.3314C330.528 6.09744 296.38 -8.06106 276.422 11.9103Z%22 fill=%22%2356E16C%22/%3E%0D%0A%3Cpath d=%22M253.896 179.567C211.574 179.567 177.218 213.863 177.218 256.255V301.43C177.218 318.827 191.367 332.985 208.794 332.985H298.999C316.467 332.985 330.574 318.827 330.574 301.43V256.255C330.574 235.08 321.985 215.897 308.127 202.029C294.31 188.12 275.099 179.567 253.938 179.567H253.896Z%22 fill=%22%2356E16C%22/%3E%0D%0A%3Cpath d=%22M121.573 179.567H31.7002C14.1904 179.567 0 193.767 0 211.289V301.222C0 329.456 34.1483 343.614 54.1061 323.643L143.979 233.71C163.937 213.738 149.788 179.567 121.573 179.567Z%22 fill=%22%2356E16C%22/%3E%0D%0A%3Cpath d=%22M497.237 336.016V2.56519H648.933C752.374 2.56519 817.559 66.2576 817.559 169.312C817.559 272.365 752.415 336.058 648.933 336.058H497.237V336.016ZM550.43 50.8535V287.77H648.933C726.026 287.77 760.838 254.927 760.838 169.312C760.838 83.6963 726.026 50.8535 648.933 50.8535H550.43Z%22 fill=%22%2356E16C%22/%3E%0D%0A%3Cpath d=%22M837.435 336.024V88.6858H886.687V155.368H890.172C897.641 115.55 924.487 83.7034 975.232 83.7034C1031.45 83.7034 1055.81 124.02 1055.81 170.813V203.158H1002.58V181.277C1002.58 145.943 987.638 129.5 950.834 129.5C908.553 129.5 891.168 152.877 891.168 197.179V336.024H837.435Z%22 fill=%22%2356E16C%22/%3E%0D%0A%3Cpath d=%22M1069.68 88.6816V336.019H1123.42V88.6816H1069.68Z%22 fill=%22%2356E16C%22/%3E%0D%0A%3Cpath d=%22M1153.24 336.024V88.6858H1202.49V163.34H1205.48C1211.95 122.027 1238.8 83.7034 1300.5 83.7034C1356.72 83.7034 1387.05 118.041 1394.02 165.333H1397.01C1403.48 123.023 1431.33 83.7034 1493.98 83.7034C1556.63 83.7034 1590.49 127.508 1590.49 187.214V336.024H1537.26V201.622C1537.26 152.835 1517.88 131.95 1470.12 131.95C1417.38 131.95 1398.5 158.814 1398.5 213.58V336.024H1345.27V201.622C1345.27 152.835 1326.39 131.95 1278.63 131.95C1225.4 131.95 1207.02 158.814 1207.02 213.58V336.024H1153.28H1153.24Z%22 fill=%22%2356E16C%22/%3E%0D%0A%3Cpath d=%22M1608.83 212.589C1608.83 135.444 1661.56 83.668 1742.14 83.668C1822.72 83.668 1870.98 125.977 1870.98 201.129C1870.98 210.098 1870.48 217.073 1868.98 224.506H1659.07C1661.06 272.296 1684.43 297.665 1741.64 297.665C1793.38 297.665 1814.75 280.724 1814.75 251.369V247.383H1868.49V251.868C1868.49 304.64 1816.74 340.971 1743.14 340.971C1662.06 340.971 1608.83 295.173 1608.83 212.548V212.589ZM1659.53 194.694H1820.19V193.697C1820.19 147.9 1793.84 126.019 1741.1 126.019C1688.37 126.019 1662.52 150.391 1659.53 194.694Z%22 fill=%22%2356E16C%22/%3E%0D%0A%3Cpath d=%22M1096.52 66.1011C1114.76 66.1011 1129.55 51.304 1129.55 33.0508C1129.55 14.7976 1114.76 0.000488281 1096.52 0.000488281C1078.28 0.000488281 1063.49 14.7976 1063.49 33.0508C1063.49 51.304 1078.28 66.1011 1096.52 66.1011Z%22 fill=%22%2356E16C%22/%3E%0D%0A%3C/g%3E%0D%0A%3Cdefs%3E%0D%0A%3CclipPath id=%22clip0_587_4308%22%3E%0D%0A%3Crect width=%221870.94%22 height=%22341.008%22 fill=%22white%22/%3E%0D%0A%3C/clipPath%3E%0D%0A%3C/defs%3E%0D%0A%3C/svg%3E%0D%0A)
%22%3E%0D%0A%3Cpath d=%22M76.678 2.56445H31.5757C14.1489 2.56445 0 16.723 0 34.12V124.386C0 141.866 14.1489 155.941 31.5757 155.941H76.7195C97.8807 155.941 117.05 147.347 130.909 133.479C144.809 119.652 153.356 100.428 153.356 79.2528C153.315 36.9019 119 2.56445 76.678 2.56445Z%22 fill=%22%23FFFFFF%22/%3E%0D%0A%3Cpath d=%22M276.422 11.9103L186.549 101.844C166.592 121.815 180.74 155.986 208.955 155.986H298.828C316.338 155.986 330.528 141.786 330.528 124.265V34.3314C330.528 6.09744 296.38 -8.06106 276.422 11.9103Z%22 fill=%22%23FFFFFF%22/%3E%0D%0A%3Cpath d=%22M253.896 179.567C211.574 179.567 177.218 213.863 177.218 256.255V301.43C177.218 318.827 191.367 332.985 208.794 332.985H298.999C316.467 332.985 330.574 318.827 330.574 301.43V256.255C330.574 235.08 321.985 215.897 308.127 202.029C294.31 188.12 275.099 179.567 253.938 179.567H253.896Z%22 fill=%22%23FFFFFF%22/%3E%0D%0A%3Cpath d=%22M121.573 179.567H31.7002C14.1904 179.567 0 193.767 0 211.289V301.222C0 329.456 34.1483 343.614 54.1061 323.643L143.979 233.71C163.937 213.738 149.788 179.567 121.573 179.567Z%22 fill=%22%23FFFFFF%22/%3E%0D%0A%3Cpath d=%22M497.237 336.016V2.56519H648.933C752.374 2.56519 817.559 66.2576 817.559 169.312C817.559 272.365 752.415 336.058 648.933 336.058H497.237V336.016ZM550.43 50.8535V287.77H648.933C726.026 287.77 760.838 254.927 760.838 169.312C760.838 83.6963 726.026 50.8535 648.933 50.8535H550.43Z%22 fill=%22%23FFFFFF%22/%3E%0D%0A%3Cpath d=%22M837.435 336.024V88.6858H886.687V155.368H890.172C897.641 115.55 924.487 83.7034 975.232 83.7034C1031.45 83.7034 1055.81 124.02 1055.81 170.813V203.158H1002.58V181.277C1002.58 145.943 987.638 129.5 950.834 129.5C908.553 129.5 891.168 152.877 891.168 197.179V336.024H837.435Z%22 fill=%22%23FFFFFF%22/%3E%0D%0A%3Cpath d=%22M1069.68 88.6816V336.019H1123.42V88.6816H1069.68Z%22 fill=%22%23FFFFFF%22/%3E%0D%0A%3Cpath d=%22M1153.24 336.024V88.6858H1202.49V163.34H1205.48C1211.95 122.027 1238.8 83.7034 1300.5 83.7034C1356.72 83.7034 1387.05 118.041 1394.02 165.333H1397.01C1403.48 123.023 1431.33 83.7034 1493.98 83.7034C1556.63 83.7034 1590.49 127.508 1590.49 187.214V336.024H1537.26V201.622C1537.26 152.835 1517.88 131.95 1470.12 131.95C1417.38 131.95 1398.5 158.814 1398.5 213.58V336.024H1345.27V201.622C1345.27 152.835 1326.39 131.95 1278.63 131.95C1225.4 131.95 1207.02 158.814 1207.02 213.58V336.024H1153.28H1153.24Z%22 fill=%22%23FFFFFF%22/%3E%0D%0A%3Cpath d=%22M1608.83 212.589C1608.83 135.444 1661.56 83.668 1742.14 83.668C1822.72 83.668 1870.98 125.977 1870.98 201.129C1870.98 210.098 1870.48 217.073 1868.98 224.506H1659.07C1661.06 272.296 1684.43 297.665 1741.64 297.665C1793.38 297.665 1814.75 280.724 1814.75 251.369V247.383H1868.49V251.868C1868.49 304.64 1816.74 340.971 1743.14 340.971C1662.06 340.971 1608.83 295.173 1608.83 212.548V212.589ZM1659.53 194.694H1820.19V193.697C1820.19 147.9 1793.84 126.019 1741.1 126.019C1688.37 126.019 1662.52 150.391 1659.53 194.694Z%22 fill=%22%23FFFFFF%22/%3E%0D%0A%3Cpath d=%22M1096.52 66.1011C1114.76 66.1011 1129.55 51.304 1129.55 33.0508C1129.55 14.7976 1114.76 0.000488281 1096.52 0.000488281C1078.28 0.000488281 1063.49 14.7976 1063.49 33.0508C1063.49 51.304 1078.28 66.1011 1096.52 66.1011Z%22 fill=%22%23FFFFFF%22/%3E%0D%0A%3C/g%3E%0D%0A%3Cdefs%3E%0D%0A%3CclipPath id=%22clip0_587_4308%22%3E%0D%0A%3Crect width=%221870.94%22 height=%22341.008%22 fill=%22white%22/%3E%0D%0A%3C/clipPath%3E%0D%0A%3C/defs%3E%0D%0A%3C/svg%3E%0D%0A)
Receive Drime Sign events with webhooks
Get an HTTP notification on your server when a document is sent, viewed, signed, declined or completed in Drime Sign, and check that each call comes from Drime.
A webhook makes Drime call your server each time something happens to your signature requests. Every call is a JSON POST, signed with a secret so your server can check it comes from Drime.
#Add a webhook
Open Settings > Developers > Webhooks.
From Sign, you can also click Preferences, open the Webhooks tab, then Open Developers settings.
Click Add webhook.
In Endpoint URL, enter the address of your server that receives the calls.
Under Events, set each event you want to receive to On, then click Create webhook.
Webhook created confirms it.
Copy the secret now, then click Done.
Webhook secret, copy it now: it is shown only once. Store it in a safe place.
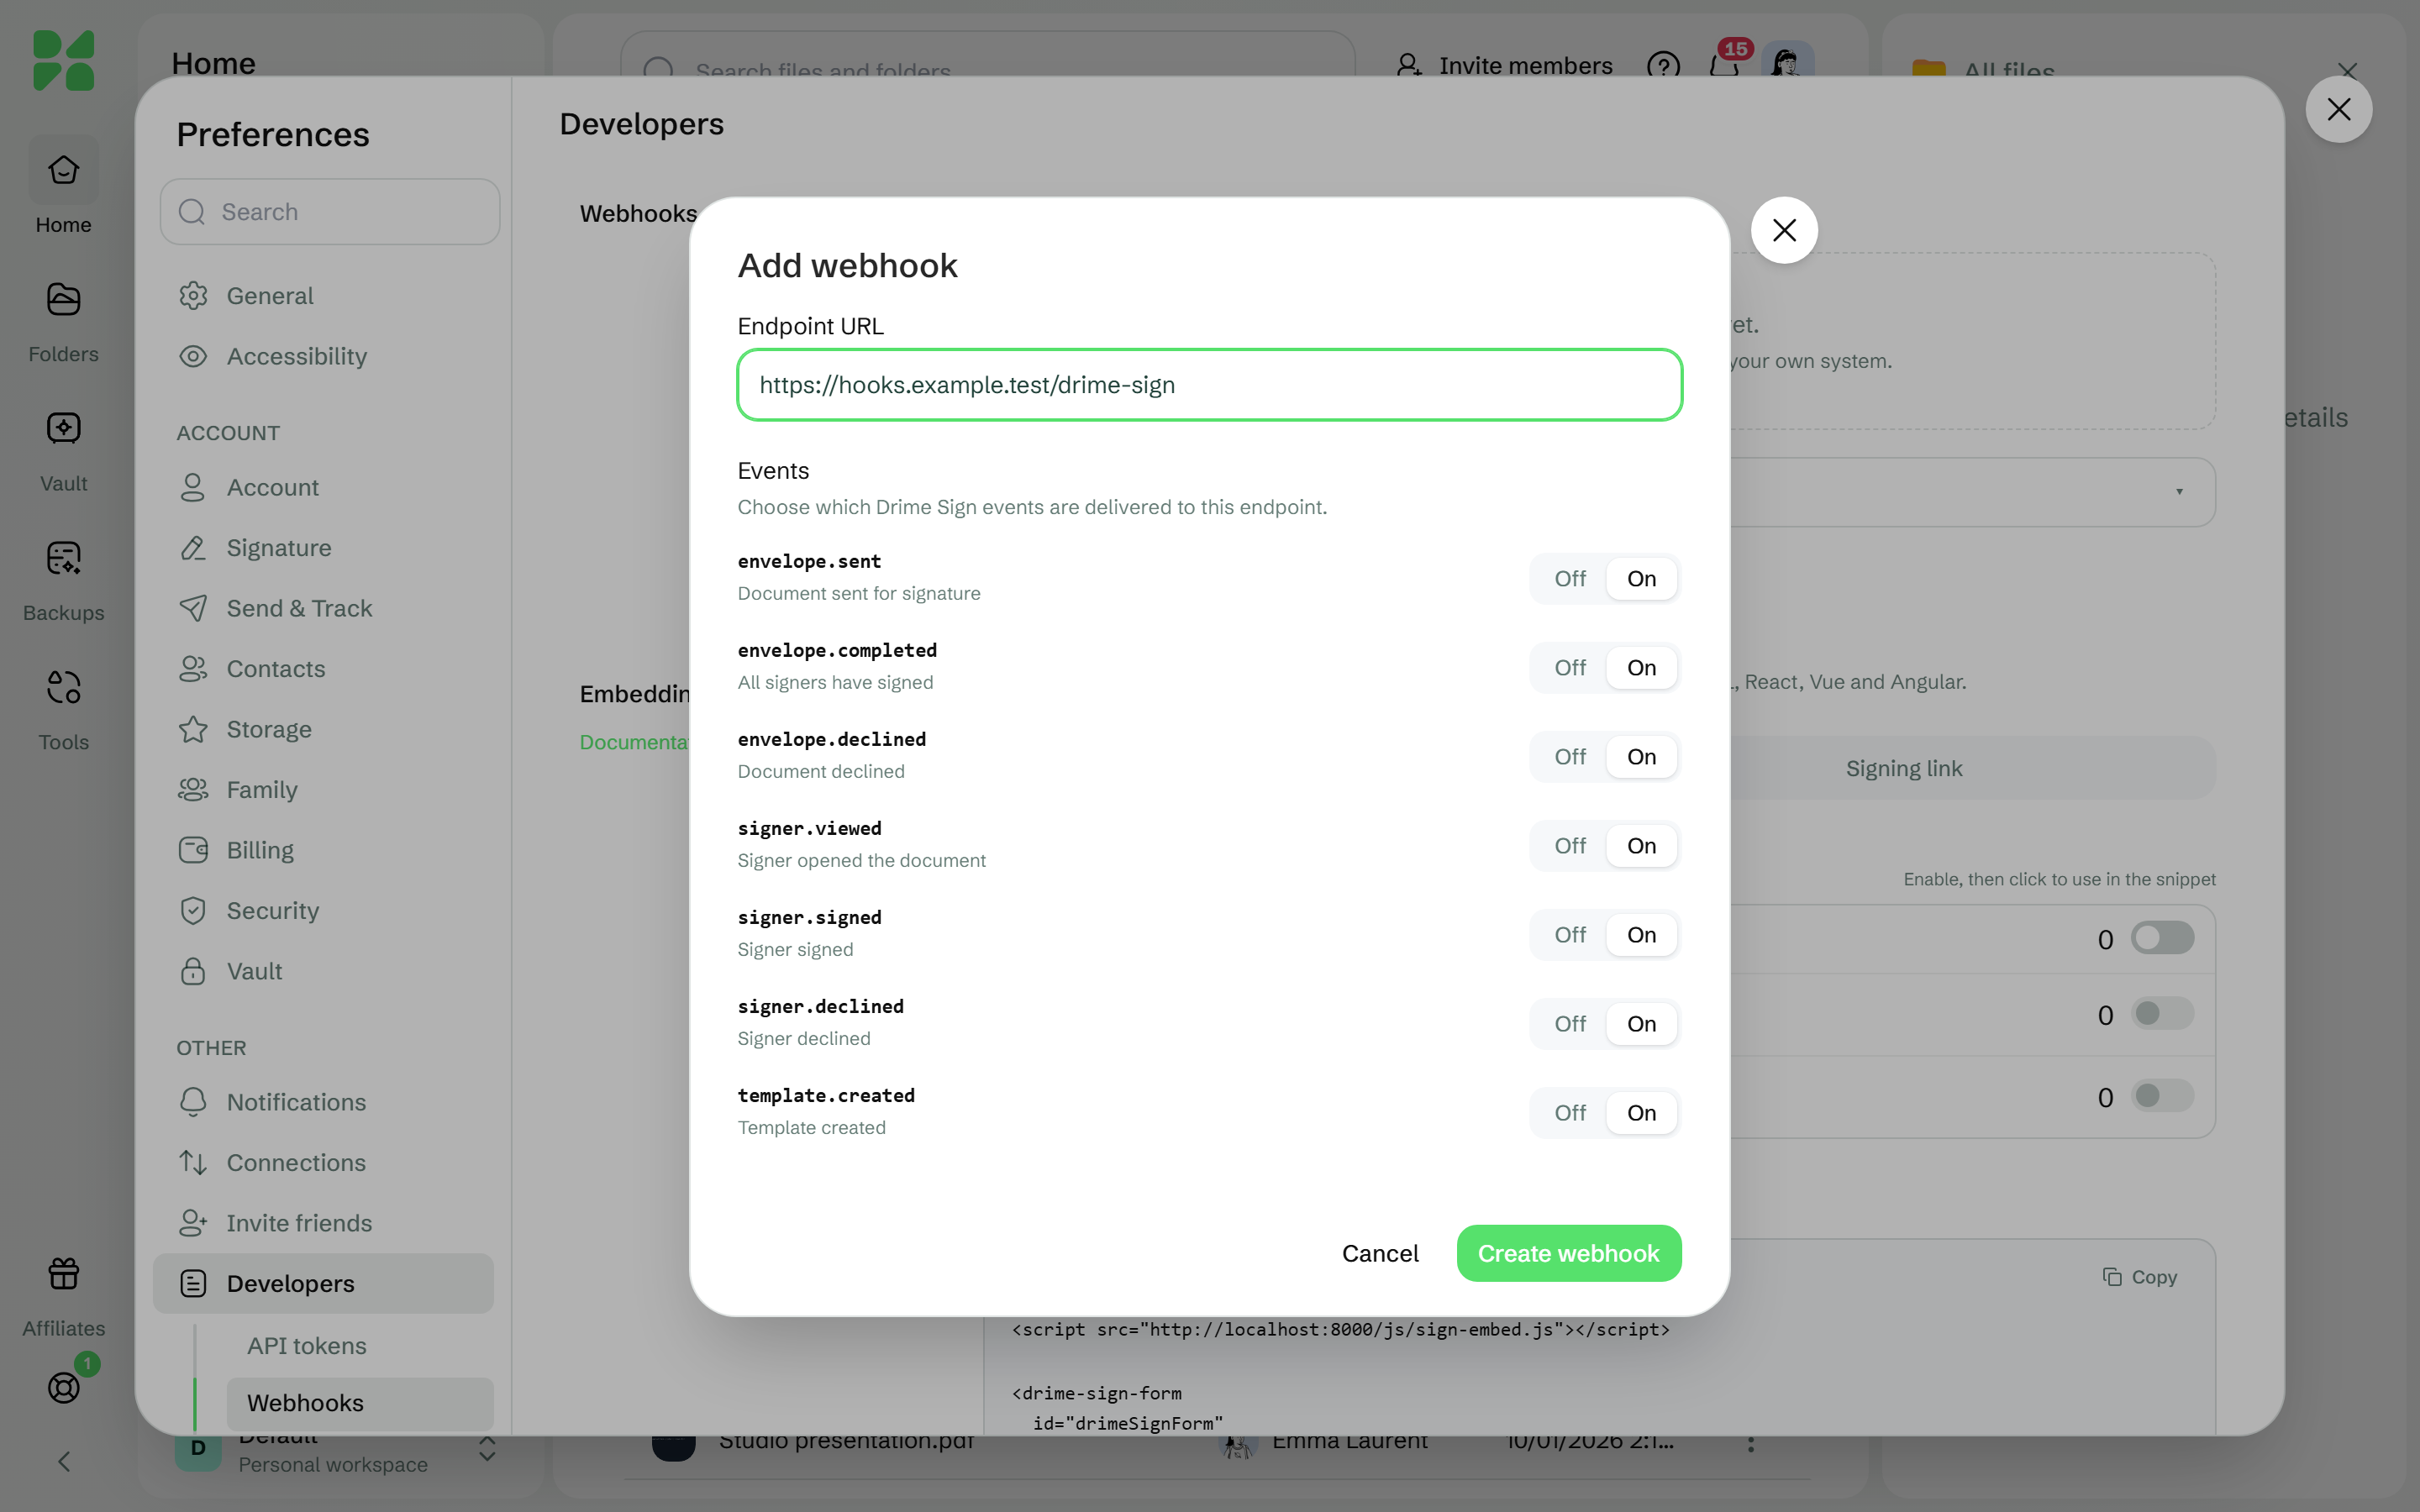
#The events
Event | Sent when |
|---|---|
| A document is sent for signature |
| All signers have signed |
| A signer declined, so the document is declined |
| A signer opened the document |
| A signer signed |
| A signer declined |
| A template is created |
#What Drime sends
Each call carries these headers:
X-Drime-Event: the event, for exampleenvelope.completed;X-Drime-Delivery: the number of the delivery;X-Drime-Signature:sha256=followed by the HMAC SHA-256 of the raw body, computed with your secret.
The JSON body holds event_type, event_uuid, timestamp and data, the document concerned with its signers. The Webhooks section shows a full example under Example request & signature verification.
A delivery can arrive more than once: use event_uuid to process each event only once.
#Check the signature
Compute the HMAC SHA-256 of the raw request body with your secret, then compare it with the X-Drime-Signature header. For example, in Node.js:
import crypto from 'node:crypto';

function isFromDrime(rawBody, header, secret) {
  const expected = 'sha256=' + crypto.createHmac('sha256', secret).update(rawBody).digest('hex');
  return header.length === expected.length && crypto.timingSafeEqual(Buffer.from(header), Buffer.from(expected));
}
Use the body exactly as received, before any JSON parsing.
#Test and follow the deliveries
Send test sends a test event: Test event queued, check the deliveries log.
Deliveries lists each call with its status: Success, Pending or Failed. Resend sends a delivery again.
If your server does not answer or answers with an error, Drime tries again, up to 10 attempts over about 34 hours.
The On / Off switch pauses a webhook without deleting it: Webhook paused confirms it, and Webhook enabled when you turn it back on.
#Change the secret or delete the webhook
Rotate secret creates a new secret. The app warns: Rotate the secret? Your current secret will stop working immediately. Update your server right away.
Delete removes the webhook: Delete this webhook and its delivery history?
#If it doesn't work
What you see | What to do |
|---|---|
Enter the endpoint URL | Enter the address of your server before you create the webhook. |
Enable at least one event | Choose at least one event under Events. |
Deliveries stay Failed | Check that your server is reachable from the internet and answers with a success code. Then click Resend. |
Your server rejects the signature | Compute the HMAC on the raw body, not on parsed JSON, and use the current secret. After Rotate secret, the old one no longer works. |
#Next steps
Was this helpful?